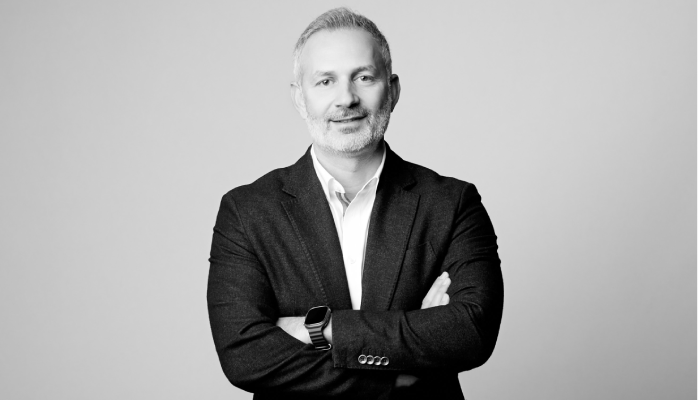
Tenable’s Walid Natour explains why interconnected cloud, identity, IT, OT and AI environments are forcing organisations to move from fragmented vulnerability management toward proactive exposure management
Enterprise cybersecurity is entering a phase where simply knowing what vulnerabilities exist is no longer enough. As organisations connect cloud platforms, identities, applications, operational technology, connected devices and increasingly AI workloads, security exposure is becoming less about individual weaknesses and more about how those weaknesses interact.
For Walid Natour, Director – Security Engineering at Tenable, this change requires a fundamental rethink of how organisations approach cybersecurity. Traditional vulnerability scanning and point solutions were designed for environments where assets, applications and risks could be assessed relatively independently. Modern enterprises, however, operate across constantly changing environments where a vulnerability in one domain can combine with a misconfiguration or excessive privilege in another to create a path to a critical business asset.
The result is an increasingly complex security landscape in which organisations may have extensive visibility but still struggle to understand which exposures represent genuine business risk.
The problem with isolated security signals
Traditional, point-in-time scanning architectures can identify vulnerabilities, but they often provide limited context about how those vulnerabilities could be combined by an attacker. At the same time, fragmented security tools generate large volumes of alerts across different domains, requiring security teams to manually correlate information before they can determine whether a particular combination of exposures represents a credible attack path.
This creates a significant operational challenge.
Security teams may know that a software vulnerability exists. They may also know that a cloud environment contains a misconfiguration, that an identity has excessive permissions or that a connected device remains insufficiently monitored. What is harder to determine is whether those conditions can be chained together to reach a sensitive application, system or other critical enterprise asset.
“Traditional, point-in-time scanning architectures and fragmented point solutions cannot keep pace with this reality because they flood security teams with uncontextualized, isolated alerts without showing how these exposures interlock,” Natour says.
This distinction is becoming increasingly important because modern attackers do not necessarily need a single critical vulnerability to compromise an organisation. Instead, they can combine several weaknesses that may appear relatively minor when viewed individually.
A software flaw can potentially be combined with a cloud configuration issue. An exposed or unmonitored connected device can provide another opportunity. Excessive identity permissions can then potentially enable lateral movement or access to higher-value resources.
The security challenge therefore shifts from asking, “What vulnerabilities do we have?” to asking, “Which combinations of exposures create a realistic path to something that matters?”
“Modern attackers rarely rely on a single isolated vulnerability. They chain together minor software flaws, misconfigured cloud buckets, unmonitored connected devices and excessive identity permissions to construct viable attack paths straight to core enterprise assets.” — Walid Natour, Director – Security Engineering, Tenable
The intersections are becoming the new attack surface
According to Natour, some of the most significant security gaps are emerging at the intersections between dynamic cloud environments, identity entitlements, shadow AI and operational technology.
Each of these domains introduces a different form of complexity.
Cloud environments are dynamic by nature, with resources and configurations changing rapidly. Identity has become a central security control as access to applications and infrastructure increasingly depends on digital identities and their associated permissions. At the same time, shadow AI introduces another layer of uncertainty as organisations adopt AI technologies and workloads alongside established IT environments.
Operational technology creates a further challenge because the consequences of compromise can extend beyond data and applications into physical processes and critical infrastructure.
The common factor is interconnection.
These environments cannot always be secured effectively when each domain is assessed independently. A vulnerability in IT may have implications for an identity. That identity may have access to cloud resources. A cloud environment may interact with operational systems or other critical infrastructure. AI workloads may introduce additional applications, data flows and access relationships.
This interconnectedness makes contextual analysis increasingly important.
Rather than treating every alert as an independent security problem, organisations need to understand the relationships between assets, vulnerabilities, identities, configurations and business-critical resources.
From reactive firefighting to exposure management
Natour argues that closing these gaps requires organisations to move away from reactive firefighting and toward preemptive exposure management.
The distinction is significant. Reactive security operations often begin after an alert has been generated, requiring teams to investigate and determine what happened, how serious it is and what action should be taken.
Exposure management seeks to understand risk before an attacker exploits it.
That requires security teams to bring different sources of security information together and analyse them in context. Natour describes this as creating a “single data fabric” through which organisations can examine cross-domain signals and identify complete attack paths.
The objective is not simply to collect more security data. It is to make the data useful for decision-making.
When security teams can see how multiple exposures interlock, they can begin to distinguish between vulnerabilities that are merely present and combinations of exposures that create material risk.
This also introduces the concept of business context.
Not every vulnerability has the same consequence. The importance of an exposure depends partly on what asset it affects, what access it provides, what other systems it connects to and what business processes ultimately depend on it.
Attack-path analysis can therefore help organisations focus limited security resources on combinations of exposures that have the potential to create meaningful business impact.
GISEC 2026: Connecting discovery with remediation
This shift from vulnerability discovery toward exposure management was also central to Tenable’s presence at GISEC Global 2026.
The company’s theme focused on helping regional organisations bridge the gap between exposure discovery and automated remediation as AI-driven threats become more advanced.
At the event, Tenable demonstrated the Tenable One Exposure Management Platform, which is designed to unify visibility across the enterprise attack surface.
That includes traditional IT environments as well as multi-cloud infrastructure, identity, OT critical infrastructure and AI workloads.
The significance of this broader coverage lies in the fact that organisations increasingly operate across all of these environments simultaneously. A security programme that focuses exclusively on endpoints or conventional IT infrastructure can leave important relationships and exposure points outside its field of view.
Tenable’s approach is therefore centred on bringing these different domains together so that security teams can understand exposure in a broader enterprise context.
AI changes the speed of security analysis
AI introduces another dimension to this challenge.
The growth of AI workloads is creating new security considerations, but AI can also change how security teams analyse and respond to exposure. At GISEC 2026, Tenable showcased capabilities including Tenable Hexa AI and AI Exposure, highlighting the use of agentic AI to analyse complex attack paths, prioritise material risks and automate mobilisation workflows.
This is important because the volume and complexity of enterprise security data can make manual analysis increasingly difficult.
Security teams must potentially evaluate vulnerabilities, identities, configurations, assets, relationships and business context across large and constantly changing environments. AI can assist in analysing those relationships and helping teams determine where attention should be focused.
However, the value of AI in this context depends on the quality and context of the underlying exposure data.
If AI is simply processing isolated alerts, it may accelerate analysis without necessarily improving the quality of the security decision. If it can instead analyse relationships across the enterprise attack surface, it can potentially help security teams understand the pathways through which an attacker could move.
That is where the convergence of exposure management and AI becomes significant.
The rise of AI exposure
AI workloads are becoming another component of the enterprise attack surface rather than a separate technology category.
Organisations are increasingly introducing AI applications, models and associated infrastructure into their environments. These workloads can interact with enterprise data, applications and identities, creating additional relationships that security teams need to understand.
For Natour, the emergence of AI therefore reinforces the need for a unified exposure-management approach.
AI security cannot be viewed only through the lens of protecting the model itself. The wider environment including identities, infrastructure, applications and access relationships also needs to be considered.
This is consistent with the broader challenge of interconnected enterprise environments: risk can emerge from the relationship between components rather than from a single component in isolation.
Prioritisation becomes critical
One of the biggest consequences of this complexity is the need to prioritise.
Organisations cannot necessarily remediate every vulnerability immediately. Security teams therefore need to determine which exposures matter most and which combinations create the greatest potential risk.
Natour’s emphasis on “material risk” reflects this requirement.
The objective is to move away from a volume-driven approach, where the number of vulnerabilities or alerts becomes the primary measure of security activity, toward a risk-driven model in which security teams focus on exposures that could create viable attack paths to important enterprise assets.
This can also improve collaboration between security and business teams.
When a security issue is presented as an isolated technical vulnerability, its business significance may be difficult to communicate. When it is presented as part of an attack path leading toward a critical asset, the potential consequence becomes easier to understand.
That creates a stronger basis for deciding which exposures should be addressed first.
A broader definition of cybersecurity
The evolution from vulnerability management to exposure management ultimately reflects a broader change in enterprise cybersecurity.
The modern attack surface is no longer confined to servers, endpoints and applications. It includes cloud infrastructure, identities, connected devices, operational technology and AI workloads. These environments are interconnected, and attackers can potentially exploit those relationships.
For organisations, the implication is that security visibility needs to become contextual rather than merely comprehensive.
Having a large inventory of vulnerabilities is useful, but understanding how those vulnerabilities combine with identities, configurations, devices and access pathways is what can turn security data into actionable risk intelligence.
Tenable’s message at GISEC 2026 was therefore not simply about adding another layer of technology. It was about changing the way organisations interpret exposure.
As enterprises become more interconnected, the security question is increasingly not where the individual weaknesses are, but how those weaknesses connect—and whether they create a path to something the organisation cannot afford to lose.
That shift from vulnerability-centric thinking to attack-path and exposure-centric thinking could become increasingly important as cloud, identity, OT and AI continue to converge within the enterprise.
