As digital transformation connects cloud, identity, IT, OT and IoT environments, Nozomi Networks says organisations must move beyond siloed security towards visibility-driven, risk-based cyber resilience.
The traditional boundaries separating IT and operational technology (OT) are rapidly disappearing. Cloud connectivity, IoT deployments, digital transformation and increasingly interconnected cyber-physical systems are creating new operational efficiencies but they are also expanding the attack surface for enterprises.
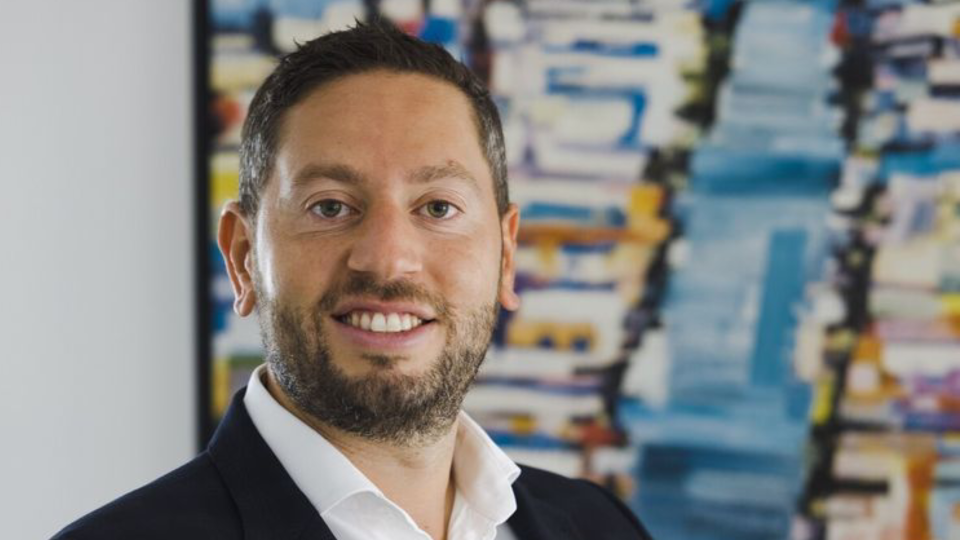
According to Bachir Moussa, Regional Vice President for EMEA South at Nozomi Networks, the greatest cybersecurity gaps are emerging at the intersections between IT, OT, IoT, cloud and identity environments.
While enterprises have generally invested heavily in securing traditional IT networks, OT and cyber-physical environments often remain less understood. The problem is not simply a lack of security controls; it is a lack of visibility, context and understanding of operational risk.
Every new connection to an asset, device, application or external organisation can potentially create another pathway into an enterprise environment. As critical infrastructure becomes increasingly digitised, a compromise that begins in an IT or IoT environment can potentially have consequences far beyond data loss including disruption to physical operations.
From Siloed Security to Integrated Risk Management
Moussa argues that organisations need to rethink cybersecurity as an integrated discipline spanning cybersecurity, operational resilience and business continuity.
The starting point is visibility. Security teams need an accurate understanding of what assets exist across OT, IoT and cyber-physical environments, how those assets communicate and where vulnerabilities or threats could translate into genuine operational exposure.
This represents an important shift from simply responding to security alerts.
An alert in isolation provides limited value unless security teams can understand which asset is affected, how critical it is, what it is connected to and what the potential operational consequences could be.
Threat intelligence and vulnerability intelligence therefore need to be connected to asset and operational context. Such contextualisation can help organisations prioritise risks rather than treating every vulnerability or security event with equal urgency.
“The intersections of IT, OT, IoT, cloud and identity systems present some of the biggest security risks for organisations today.”
— Bachir Moussa, Regional Vice President, EMEA South, Nozomi Networks
AI Can Strengthen Context Not Replace It
Artificial intelligence is emerging as an important capability in this environment, particularly as security teams contend with increasingly large volumes of data and alerts.
However, AI is most effective when it operates on reliable and contextualised information.
For OT and cyber-physical environments, that means organisations first need to establish visibility across their assets and understand communication patterns, dependencies and vulnerabilities. AI can then help security teams process this information, identify relevant patterns and accelerate investigation and decision-making.
The strategic priority, therefore, is not simply deploying AI for cybersecurity. It is building the data, visibility and context required to make AI useful for security operations.
Nozomi Networks Brings OT Security Focus to GISEC 2026
At GISEC Global 2026, Nozomi Networks will focus on helping organisations strengthen resilience across OT, IoT and cyber-physical systems.
The company’s approach centres on three priorities: visibility, context and actionable information.
Rather than concentrating solely on security alerts, the objective is to help security teams understand their environments, assess exposure and manage threats based on their potential impact.
Nozomi Networks will showcase AI-driven capabilities spanning asset visibility, threat intelligence, vulnerability management and threat detection. The demonstrations are designed to show how asset and threat intelligence can be translated into meaningful security outcomes in real operational scenarios.
Among the capabilities being highlighted is Vantage IQ Assistant, an AI-powered security assistant for OT and IoT environments. It enables security teams to interact with security information using natural language and obtain context-aware answers covering assets, threats, risk, investigations and reporting.
The New Cybersecurity Imperative: Understand Before You Respond
The convergence of IT and OT is changing what enterprise cybersecurity needs to achieve. Protecting the network perimeter is no longer enough when business-critical operations depend on interconnected devices, industrial systems, cloud platforms and digital identities.
The emerging security model is consequently less about defending isolated environments and more about understanding the entire cyber-physical ecosystem.
For organisations operating critical infrastructure, manufacturing, energy, transportation and other operationally sensitive environments, this distinction is particularly important. Cybersecurity decisions increasingly need to account for operational continuity and business impact not just technical indicators of compromise.
The lesson from the expanding attack surface is clear: visibility must come before prioritisation, context before response, and risk before remediation.
As enterprises continue connecting more systems, devices and identities, the organisations best positioned to withstand the next generation of cyber threats will be those that can see across these boundaries and understand how digital risks translate into real-world operational consequences.
