Security firm warns users to update Google Chrome immediately
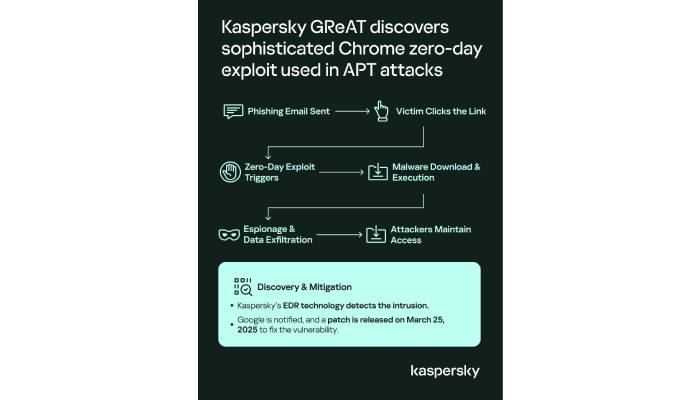
Kaspersky has uncovered a highly advanced zero-day vulnerability in Google Chrome that allowed attackers to bypass critical security protections with minimal user interaction. The flaw, identified as CVE-2025-2783, was used in a targeted espionage campaign dubbed “Operation ForumTroll.”
“This vulnerability stands out among the dozens of zero-days we’ve discovered,” said Boris Larin, principal security researcher at Kaspersky GReAT. “The exploit bypassed Chrome’s sandbox protection without performing any obviously malicious operations—it’s as if the security boundary simply didn’t exist.”
Google has patched the flaw as of March 25, 2025, and urges all users to update their browsers immediately.
