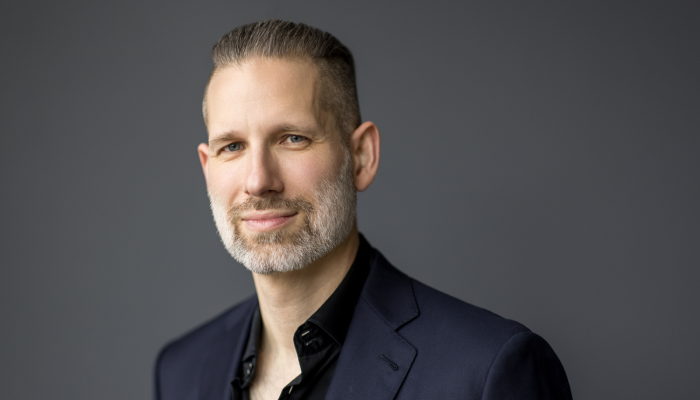
Artificial intelligence is fundamentally changing the cybersecurity landscape, giving attackers the ability to identify vulnerabilities, connect weaknesses and execute attacks at unprecedented speed. While organisations are investing heavily in understanding AI’s offensive potential, their defensive capabilities are not always keeping pace. Long-standing security gaps, unresolved vulnerabilities and fragmented visibility are becoming increasingly exploitable as AI removes many of the traditional barriers to launching attacks. Henrik Smith, Chief Information Security Officer at Infoblox, argues that organisations must rethink their approach to cyber defence, giving security teams the resources, intelligence and AI-powered capabilities they need to match the speed and sophistication of modern threats.
Artificial intelligence has changed the cybersecurity equation. But perhaps not in the way many organisations expected. Much of the discussion around AI and security has focused on what is new: autonomous agents, increasingly sophisticated models and the prospect of AI-powered systems operating with greater independence. Yet the more important shift is not necessarily that attackers have discovered entirely new vulnerabilities. It is that they can now discover, combine and exploit existing weaknesses at a speed that defenders have never had to contend with before. That changes the risk calculation.
For years, organisations have accumulated security backlogs. Access controls that needed tightening, vulnerabilities that were known but considered low priority, systems that required additional monitoring and weaknesses that were understood but never quite made it to the top of the list.
Historically, attackers faced a practical limitation: exploiting these weaknesses at scale required time, effort and coordination. AI is rapidly reducing that constraint. An attacker can now test huge numbers of possibilities, identify combinations of weaknesses and refine an attack chain far more quickly. What might previously have required days to months of planning can potentially be compressed dramatically. At the same time, defensive teams are still expected to detect, investigate, prioritise and remediate those activities using processes that were designed for a slower environment. This creates an uncomfortable imbalance.
The cybersecurity industry has spent considerable effort building sophisticated offensive capabilities. Organisations regularly highlight the capabilities of their red teams, penetration testing programmes and offensive security specialists. These activities are important. But there needs to be an equivalent commitment on the defensive side.
If offensive teams are using advanced technologies to discover how an organisation can be breached, defensive teams need comparable budget, staffing and expertise to understand how those techniques can be detected and stopped. This is where AI should become more than another technology initiative. It should become an operational capability.
The opportunity is particularly significant when AI is used to address the security work that organisations have historically struggled to complete. AI and autonomous agents can process enormous volumes of information, identify patterns and correlate seemingly insignificant signals across an environment. Used appropriately, they can help security teams work through backlogs, identify gaps and prioritise the issues that genuinely affect an organisation’s risk posture. For now, however, GenAI is benefiting attackers more than defenders. The defensive advantage will only emerge if organizations invest in the people, processes and systems needed to use it operationally.
“AI is changing the speed of the game. The organisations that adapt will not necessarily be those with the most AI projects. They will be those that understand where AI can deliver genuine security value and use it to close the gaps that already exist.”
Henrik Smith, Chief Information Security Officer, Infoblox
One of the biggest challenges facing organisations is resourcing and prioritisation. Security teams are often operating under pressure, while development and business teams continue to move rapidly. The result can be a familiar imbalance: large numbers of people and resources focused on building and deploying new capabilities, alongside comparatively limited resources dedicated to securing them. AI does not eliminate that imbalance. It makes it more visible.
Organisations therefore need to rethink how security teams work together. Offensive and defensive functions should not operate as separate worlds. The lessons generated by offensive testing should feed directly into defensive controls, detection and remediation. If an offensive capability identifies a new way into an environment, the defensive team should be able to use that information immediately to strengthen the organisation’s protection.
The same principle applies to basic security hygiene. There is a tendency to think that sophisticated AI attacks require sophisticated AI defences. In reality, many of the weaknesses being exploited are remarkably familiar. Poor access controls, excessive privileges, unresolved vulnerabilities and fragmented visibility remain important problems. AI simply makes it easier for an attacker to find and exploit the gaps that organisations have allowed to remain in place.
That means the definition of “acceptable risk” may also need to change. A vulnerability that was previously classified as low risk because it was difficult to exploit may no longer deserve that classification. A collection of individually minor weaknesses can become significant when an attacker has the ability to correlate them and move rapidly between them.
Security leaders therefore need to understand their risk posture as a connected system rather than a collection of individual alerts.
This also requires organisations to be cautious about getting distracted by the latest AI headline. The cybersecurity industry does not need another cycle of hype in which organisations sign declarations, join coalitions or announce initiatives without demonstrating what those commitments actually deliver.
Collaboration matters. But meaningful collaboration is measured by outcomes: information shared, vulnerabilities addressed, attacks detected, controls improved and response times reduced.
The same principle should apply to responsible AI. The conversation cannot simply be about whether an AI agent behaves unexpectedly. Organisations need to ask why that behaviour was possible in the first place. Was the agent given excessive access? Were controls insufficient? Was there inadequate monitoring? Were basic security practices overlooked?
AI is changing the speed of the game. The organisations that adapt will not necessarily be those with the most AI projects. They will be those that understand where AI can deliver genuine security value and use it to close the gaps that already exist.
The priority now should be straightforward: give defenders the resources, capabilities and intelligence they need to move at a pace closer to the attackers.
The era of accepting security backlogs as simply part of doing business is coming to an end. In an environment where AI can turn yesterday’s minor weakness into tomorrow’s attack path, organisations can no longer afford to leave known problems waiting for another day.
Bio of Author
Henrik Smith is Chief Information Security Officer at Infoblox, where he leads the company’s global security strategy, cyber resilience and risk management initiatives. He brings nearly 30 years of cybersecurity leadership experience, having previously served as Head of Security for Devices and Services at Amazon and Vice President of Security at Salesforce. Earlier in his career, he held several leadership positions within AWS Security and was a founding member of both the Office of the CISO and Security Assurance organisations. His expertise spans cloud security, enterprise security, risk management and cybersecurity strategy.
