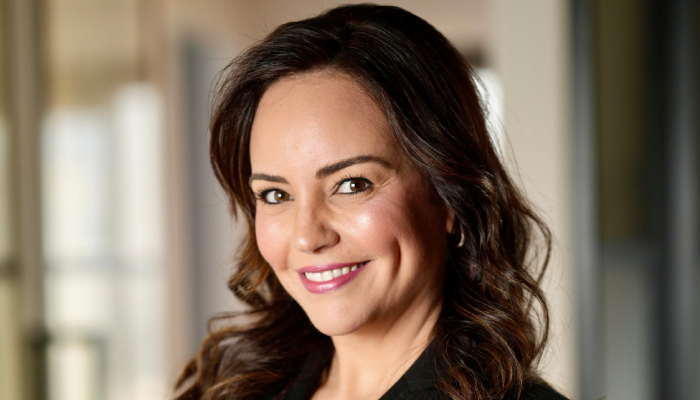
Meriam ElOuazzani, Vice President for Middle East, Turkey, and Africa, Censys discusses how rapidly malware signature-based detections become obsolete due to the constant modification of both toolsets and tactics used by hackers. By analyzing repetitive attack patterns in Internet-exposed infrastructures, security analysts can identify threats ahead of time before any malware is mentioned in threat intelligence sources.
Cyber attackers rarely use the same techniques for long. By the time a new strain of malware is found, they may have already moved on to the next tactic, having altered their infrastructure, modified their code, or switched to other delivery methods to avoid detection. This means security teams have to pursue threats that have long since changed. The quicker security teams identify the methods being used by an attacker, the quicker they can take the right action.
The rise of web-delivered attacks
Web-based attacks typically start on sites that appear legitimate. The attackers then use them to send out harmful scripts or to trick victims into carrying out their instructions. Such attacks can come in many forms, including the use of fake login pages and misleading verification messages, as well as automated script execution and social engineering. Since these threats are constantly evolving, it has become more important than ever to monitor behavioral indicators in web environments, this can then enable security teams to detect activity that signature-based detection methods may otherwise fail to pick up.
Limitations of signature-based detection
Signature-based detection is the backbone of enterprise security today. Many security products still use known indicators like malware hashes, domains, and previously identified attack patterns. This approach only works once a threat has already been seen and documented. It also struggles when malware is slightly modified or when attackers introduce new delivery methods. These gaps create opportunities for attackers to bypass defenses with small but effective changes. As threats evolve, it struggles with previously unseen threats, including AI-generated attacks.
Even with its limitations, it was the best way to catch common malware with minimal false positives. When a file matches an existing signature, it can be immediately flagged before it can spread. For security teams, this means they have the confidence to deal with the threat, knowing that it is genuine.
“It is important to focus on identifying patterns and correlating multiple weak signals across internet-facing infrastructure.”
Meriam ElOuazzani, Vice President for Middle East, Turkey, and Africa at Censys
Shifting the focus from malware variants to attacker techniques
Malware names and signatures are a moving target. Attackers may swap a payload, repack a loader, or set up a new domain within minutes, but the underlying techniques they are dependent on to deliver that malware change far more slowly. For example, fake verification prompts, disguised download pages, obfuscated scripts hidden in web content, and multi-stage redirect chains may consistently reappear across varying websites. Rather than chasing every new variant, it would be far more effective for security teams to get ahead of these attackers by keeping a close eye on the public web for recurring techniques as they surface on live infrastructure.
This is where internet intelligence enters the picture. By observing internet infrastructure, security teams will be able to detect threats and their methods even before they get picked up by intelligence feeds.
The effectiveness of technique-based hunting
It is important to focus on identifying patterns and correlating multiple weak signals across internet-facing infrastructure. These technique-level indicators expose the malicious infrastructure behind them. This enables security teams to separate real threats from noise, spot campaigns sooner, and begin their investigations before the infrastructure shows up in intelligence feeds or is associated with any known threat actor or malware family.
That is the advantage of searching techniques over matching signatures. Organizations can proactively identify and disrupt threat campaigns. Defenders can now discover malicious activity earlier in the life cycle, avoiding continually having to react to an endless stream of malware variants and delivery methods, which signature-based detection alone is unable to keep up with.
