Optro’s 2026 agentic enterprise report finds that enterprises are granting AI agents authority over transactions, controls and user access, while only 9% have redesigned workflows to govern their actions safely.
Enterprise adoption of artificial intelligence is entering a more consequential phase, moving beyond tools that generate recommendations or assist employees to systems authorised to make decisions and execute actions independently. But as AI agents gain operational authority, organisations are struggling to establish the governance and oversight needed to manage the risks.
A new report from Optro, titled Authority without oversight: The 2026 agentic enterprise report, highlights this widening gap between AI deployment and organisational readiness. Based on a survey of 417 governance, risk, compliance and audit leaders, the research finds that 34% of organisations have experienced an inaccurate AI agent decision or output that employees acted upon.
The finding points to a critical governance challenge: an incorrect AI-generated response is no longer merely a quality issue when an agent can approve a transaction, modify a control or change a user’s access rights. Once connected to enterprise workflows, an agent’s decision can have direct operational, financial, security and regulatory consequences.
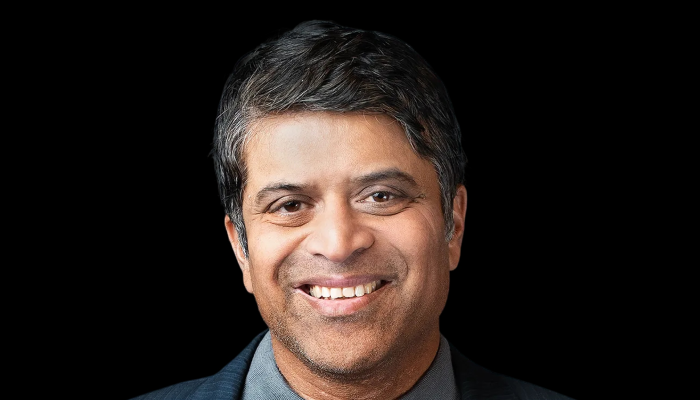
“Enterprise AI agents are now embedded directly into workflows with real business, compliance, and regulatory consequences,” said Guru Sethupathy, GM of AI Governance at Optro. “This report underscores the need for a disciplined operating model where agent authority matches an organization’s ability to govern it.”
Enterprise authority is expanding faster than oversight
The research suggests that organisations are already assigning AI agents responsibilities that were traditionally subject to human approval or established control processes. According to the report, 38% of respondents said their organisations authorise agents to approve or reject transactions. Another 34% allow agents to modify controls or policies, while 27% permit them to change user permissions or access rights.
These are not routine productivity functions. Transaction approvals can affect financial exposure, policy modifications can change how controls operate, and access-right changes can influence the security of enterprise systems and information.
The implications become more significant when agents operate across interconnected applications. An agent’s decision in one workflow may influence another system, trigger a subsequent action or alter the information available to employees. Without clearly defined boundaries, an error can move beyond the point at which it originated.
The concern is not simply whether an AI agent produces an inaccurate answer. It is whether the organisation has the ability to prevent that answer from becoming an unauthorised or harmful business action.
Optro’s findings indicate that these risks are already materialising. Alongside the 34% reporting that an inaccurate agent decision or output was acted upon, 30% have seen an AI agent take an unintended action, while 25% have experienced a control failure involving an agent.
Together, these findings suggest that agentic AI governance needs to address both the quality of an agent’s decisions and the authority it has to execute them.
“Enterprise AI agents are now embedded directly into workflows with real business, compliance, and regulatory consequences.”
— Guru Sethupathy, GM of AI Governance, Optro
The workflow redesign gap
Perhaps the most striking finding is the difference between the enthusiasm for AI adoption and the extent of operational change required to support it safely.
The survey found that 96% of leaders agree workflows should adapt to take advantage of AI capabilities. Yet only 9% said their organisations have redesigned workflows to accommodate AI agents safely.
This gap raises questions about how enterprises are integrating agents into existing processes. Many organisations may be introducing AI capabilities into workflows designed around human decision-making, approval hierarchies and established accountability structures. Those processes may not adequately account for agents that can initiate or complete actions independently.
A workflow designed for an employee who reviews information before making a decision may not be suitable for an autonomous agent operating at greater speed and scale. Organisations need to determine which decisions can be delegated, which require human approval and which actions should remain outside an agent’s authority.
The findings also suggest that AI adoption cannot be measured solely by the number of agents deployed or the tasks automated. The quality of workflow redesign, the clarity of decision rights and the ability to monitor actions are equally important indicators of readiness.
AI is not necessarily reducing employee workload
The assumption that AI agents automatically reduce operational effort is also challenged by the report. Nearly half of respondents, 46%, said employees are spending more time reviewing, validating or correcting AI outputs.
This suggests that automation can shift work rather than eliminate it. Employees may spend less time generating information or completing repetitive tasks but more time checking whether an agent’s output is accurate, appropriate and safe to use.
The additional review burden may be particularly difficult to manage when organisations deploy agents across multiple departments and business processes. If employees must validate every action without clear risk-based controls, the expected productivity gains may be diluted by the effort required to supervise the technology.
It also creates a question of accountability. Employees need to understand when they are expected to approve an agent’s decision, when they can rely on its output and how they should escalate an action that appears incorrect. Without clearly defined responsibilities, human oversight can become an informal checkpoint rather than a dependable control.
Traditional GRC systems face a new challenge
The report places these developments within a broader shift in enterprise risk. AI, cybersecurity, operational and regulatory threats are increasingly interacting, while organisations continue to rely on governance, risk and compliance architectures that may not provide sufficiently current visibility.
Optro argues that traditional GRC systems often function as static, backward-looking systems of record. According to the company, this can leave organisations up to three months out of date, creating a gap between the risks they have documented and the conditions under which their businesses are actually operating.
That limitation becomes more pronounced when AI agents can change policies, execute transactions or alter access rights. A risk register or control assessment that does not reflect current operational activity may provide an incomplete picture of the organisation’s exposure.
The challenge is to connect governance information with the actions taking place across enterprise systems. Organisations need to know what agents are authorised to do, which controls apply to their activities, what decisions they have made and whether those decisions have produced the intended outcomes.
Optro positions its GRC Intelligence Platform as an approach to this problem, combining what it describes as a trusted system of record with an intelligent, agentic system of action. The company’s proposition is to bring governance information and operational action closer together, although the report’s findings do not independently establish the effectiveness of any particular platform.
Governance must match the authority given to agents
The central lesson from the research is that agentic AI requires a more deliberate operating model. Organisations cannot simply extend the permissions of existing employees or applications to AI agents without considering the risks created by autonomous decision-making.
A governance framework needs to define the limits of each agent’s authority. It should establish which actions can be performed independently, which require human approval and which are prohibited. These boundaries should reflect the potential business impact of an action rather than treating every automated task as equally risky.
Organisations also need to maintain visibility into agent activity. This includes understanding what information an agent can access, which systems it can interact with, what decisions it makes and whether its actions can be traced and reviewed. When an agent changes a control or user permission, the organisation should be able to establish why the action occurred and whether it was authorised.
Human oversight remains important, but it needs to be designed into the workflow. Requiring employees to review every output may create additional operational friction. A more sustainable approach would distinguish between routine, low-risk actions and decisions that carry significant financial, regulatory, security or operational consequences.
The report’s findings also reinforce the need to test agentic workflows before granting them broad authority. Organisations should assess how agents behave when information is incomplete, instructions conflict or a task falls outside the intended scope. They should also establish procedures for suspending an agent’s activity and reversing or correcting unintended actions.
Methodology and the road ahead
Optro’s research is based on a 2026 survey of 417 respondents recruited through a global online panel provider. Participants were enterprise-level decision-makers working in Internal Audit, Risk Management, Compliance and Governance, and Information Security across North America and Europe. All respondents represented organisations with at least 250 employees and were vetted for their knowledge of agentic AI. The research also included qualitative interviews with members of Optro’s Customer Advisory Board.
The findings offer a snapshot of how enterprise leaders are managing the transition to agentic AI. While the survey does not establish that every organisation faces the same level of exposure, the reported experience of inaccurate decisions, unintended actions and control failures indicates that governance challenges are no longer theoretical.
The next stage of enterprise AI adoption will depend on whether organisations can align the authority given to agents with the controls required to supervise them. Deploying agents without redesigning workflows risks creating a new layer of operational complexity, where automated decisions move faster than existing governance processes can respond.
For enterprises, the priority is therefore not simply to accelerate agent deployment. It is to establish clear accountability, controlled permissions, continuous monitoring and effective intervention mechanisms before agents are entrusted with decisions that carry material consequences.
The Optro research captures the emerging dilemma of the agentic enterprise: organisations want AI to act with greater independence, but they must ensure that autonomy does not come at the expense of control.
